Agent Governance
Zero-trust guardrails for deploying AI agents to production: ephemeral credentials, policy enforcement, and FinOps controls.
The problem
AI agents are easy to build, but difficult to trust in production. They hold long-lived credentials, have broad access to sensitive data, and can rack up thousands in API costs in a matter of minutes.
The solution
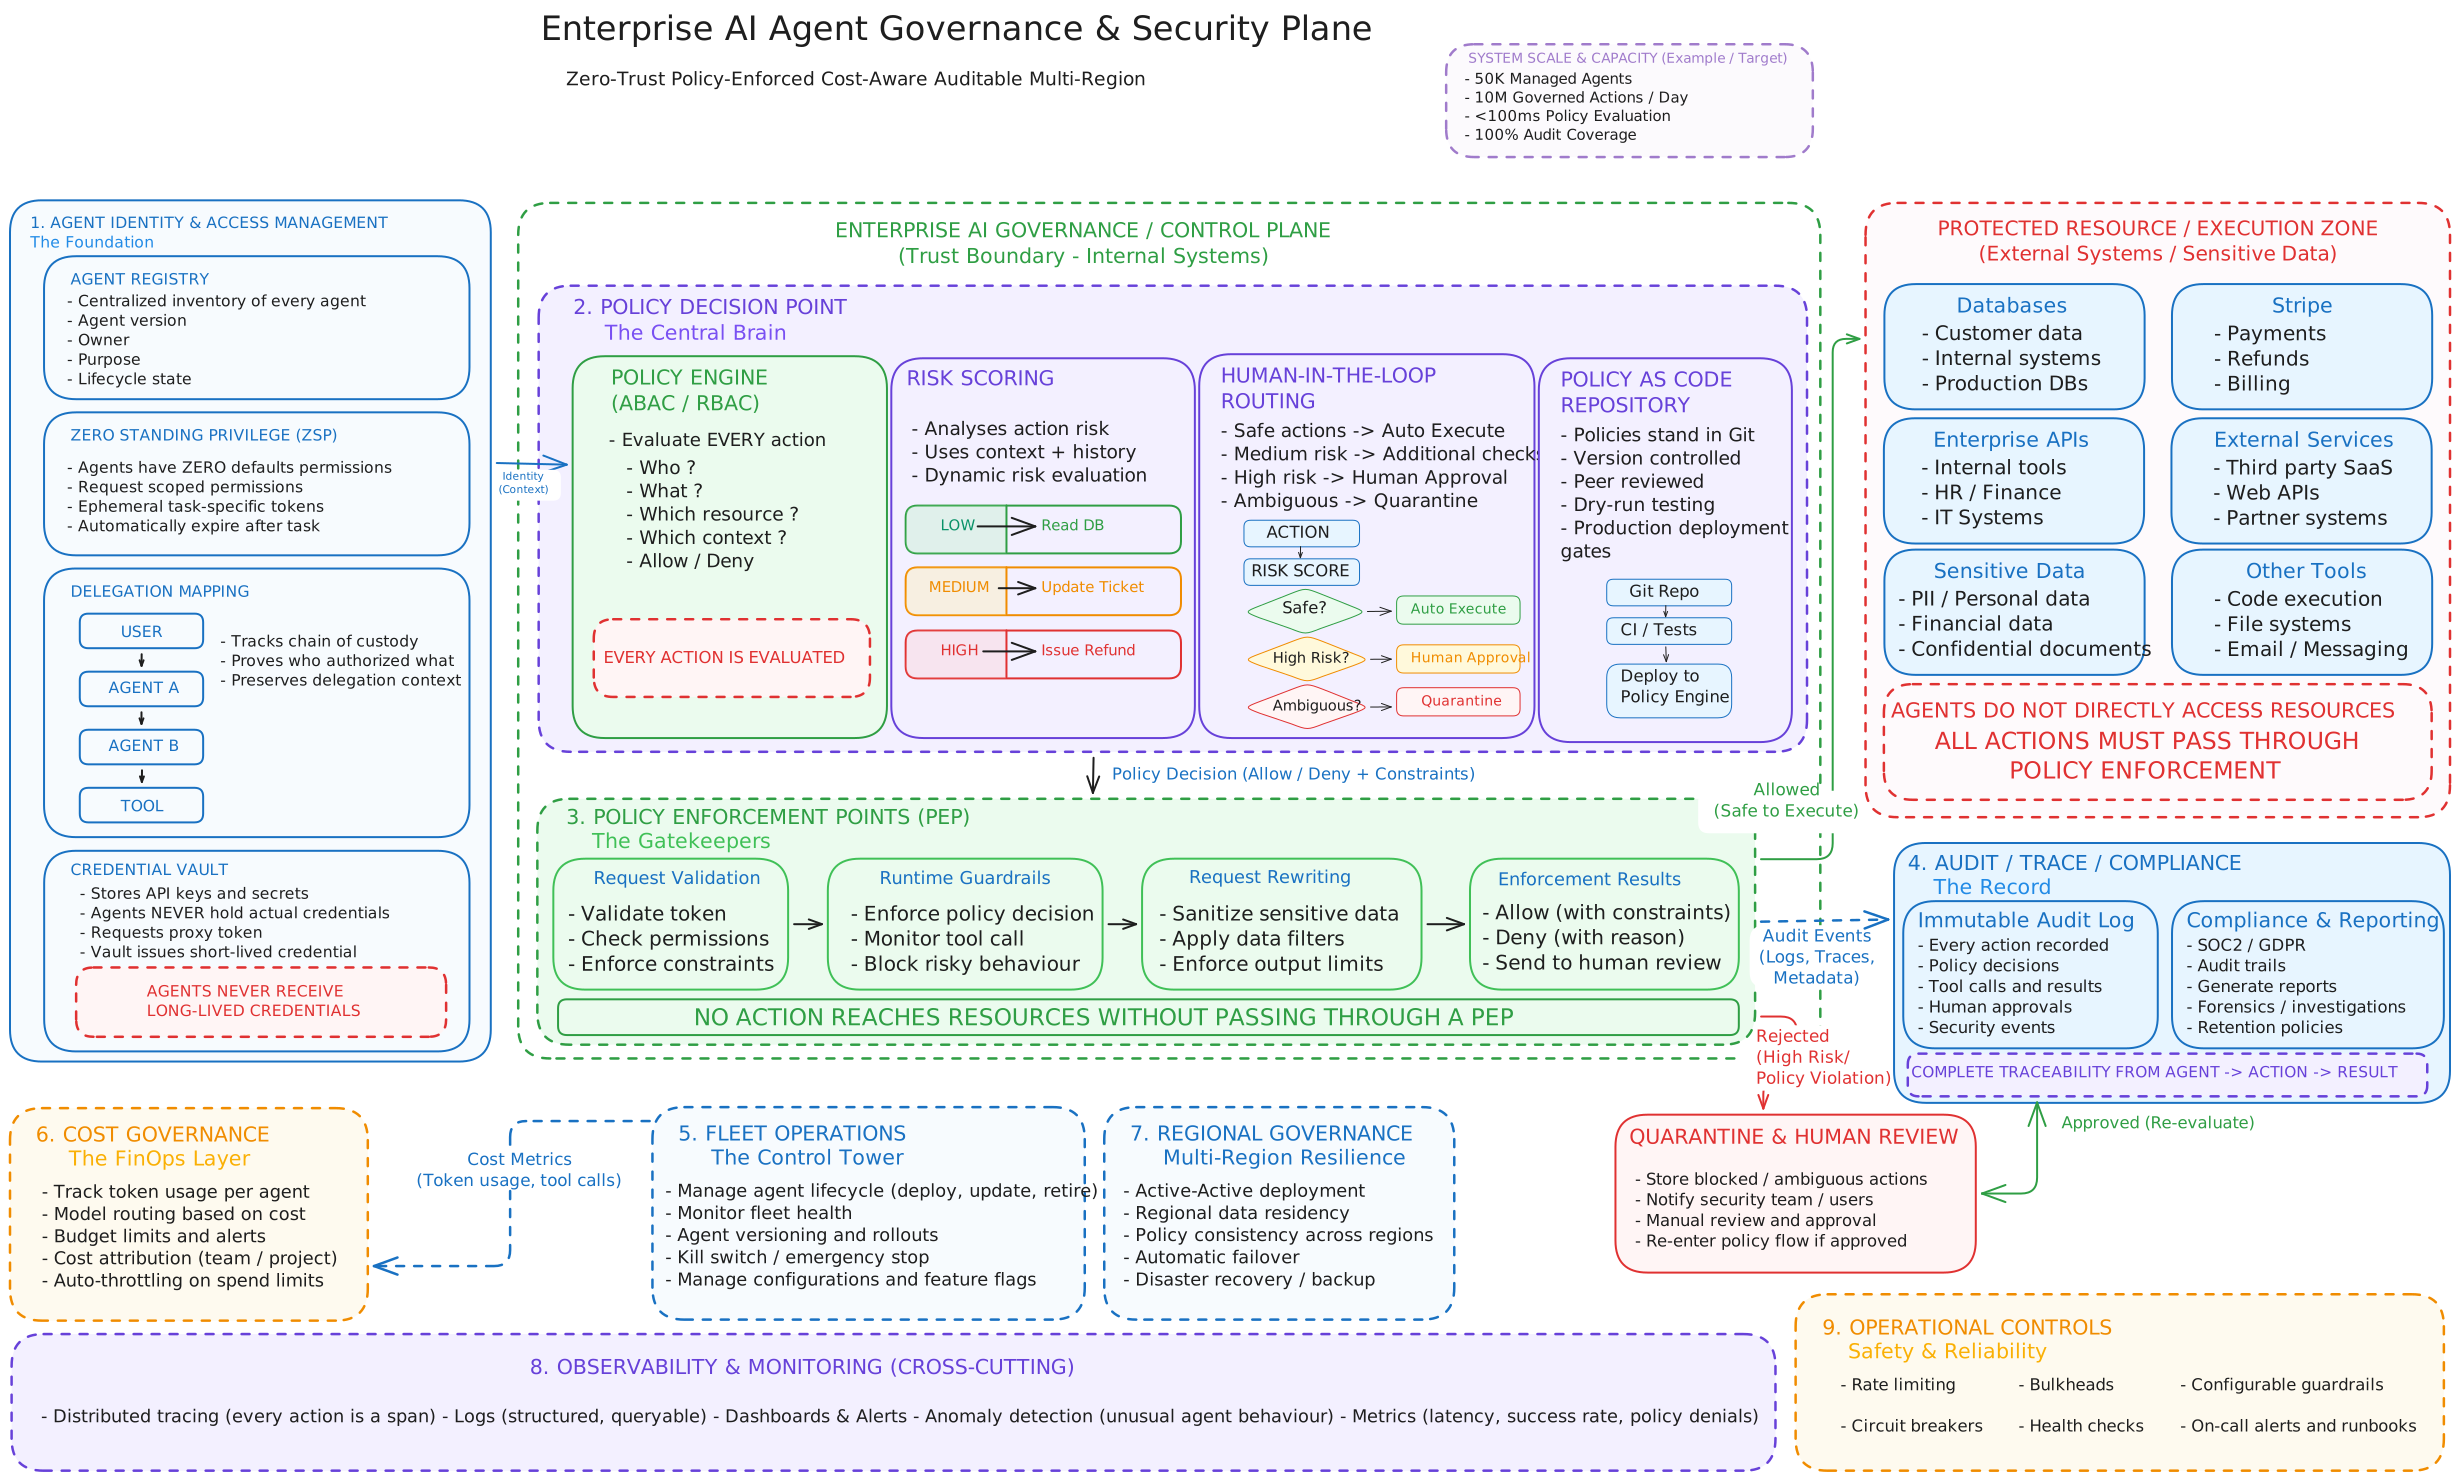
An Enterprise AI Agent Governance & Security Plane built on Zero-Trust principles. This is not just an orchestrator; it is a control tower that sits between your agents and your protected resources.
Core capabilities
Zero Standing Privilege (ZSP)
Agents never hold real credentials; they request ephemeral, task-scoped tokens that expire automatically.
Policy Enforcement (PDP/PEP)
Every action is evaluated before execution. Low-risk tasks auto-execute; high-risk tasks route to human-in-the-loop.
FinOps for AI
Real-time token tracking, model routing based on cost, and hard budget limits to prevent runaway API expenses.
Multi-Region & Audit
Immutable traceability of every thought, tool call, and action across regions.
Why this matters
It allows companies to deploy autonomous agents to production fast, without compromising security, blowing the budget, or breaking compliance.
